November 19, 2026: The Java4Shell vulnerability (CVE-2026-114938) affects the Java runtime environment. We have assessed its impact on anynode and consider the risk to our customers to be low. We are currently unaware of any specific attacks on anynode installations.
As a precaution, starting with anynode version 4.14.25, we are providing a protective measure that disables the affected Java processing path.
What is Java4Shell?
Java4Shell is a flaw in the processing of Base64-encoded data in certain Java runtime environments. Specially crafted input can corrupt memory. This can cause applications to crash, expose confidential information, or, under certain conditions, allow arbitrary code to be executed. Exploitation requires specific processor features and manipulated data to reach the affected processing path.
Results of our assessment
We examined all of our code and found no affected code paths in our software. We process the relevant data through our own path, which is not affected by this vulnerability.
One exception concerns the optional sign-in using a Microsoft/Azure account (Entra ID) in the anynode Frontend. For this, we use a third-party component that uses the affected processing path in the Java runtime environment.
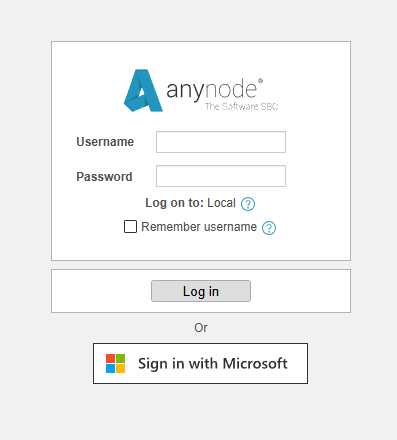
anynode Frontend with Microsoft Entra ID sign-in
Why we consider the risk to be low
Based on our assessment, a risk through this sign-in path would only be conceivable if the endpoint to which the Frontend connects were untrustworthy—for example, a manipulated or intermediary sign-in service. This condition does not apply during normal operation with the trusted Microsoft service.
In addition, the sign-in option would have to be actively used, and further specific technical conditions would have to coincide. We are unaware of any specific attack on an anynode installation.
Automatic protective measure starting with version 4.14.25
Despite the low probability, we are taking precautionary measures: Starting with version 4.14.25, we disable the affected Java processing path using the runtime option -XX:-UseBASE64Intrinsics. This protective measure also covers the third-party component we use.
The setting takes effect automatically with the update. No additional configuration is required on your part.
anynode version 4.14.25 will soon be available for download in our Community.
Current status of Java fixes
On Windows, anynode 4.14.24 includes the Eclipse Temurin 17.0.20.1+1 Java runtime environment from Eclipse Adoptium.
Java fixes have already been released for various distributions and platforms. However, the required Temurin version for Windows x64 has not yet been released. Adoptium lists 17.0.21.1+2 as the fixed Temurin version; according to the official status overview, testing for Windows x64 is still ongoing. Vendor advisory, Release status
Once the corresponding fixed runtime is available, we will update our bundled Java in one of the next anynode releases. This will permanently resolve the underlying issue, allowing the temporary disabling to be removed.
Note for Linux installations
If your Linux installation uses the operating system’s Java, please update it through the regular package manager as soon as your operating system vendor provides a fixed version.
What you should do now
Install anynode 4.14.25 as soon as the version is available in our Community. The protective measure is automatically active in this version; you do not need to change any Java settings yourself.
We are monitoring further developments and incorporating new findings into our releases.